AI didn’t enter your enterprise through one door
See how AccuroAI discovers every AI tool and agent, redacts sensitive data in line, and blocks risky agent actions before they reach your systems.

Ratings as of Aug 7, 2026. Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates.
Five problems.
One control plane.
The risks converge faster than point tools can. AccuroAI covers all five with one policy engine and one audit trail.
One platform. Every surface.
Workforce tools, autonomous agents, local endpoints. AccuroAI covers all three.
One console. However you enter.
Whichever product you start with, this is where you land: one dashboard, one policy engine, one audit trail across governance, agents, and every device.
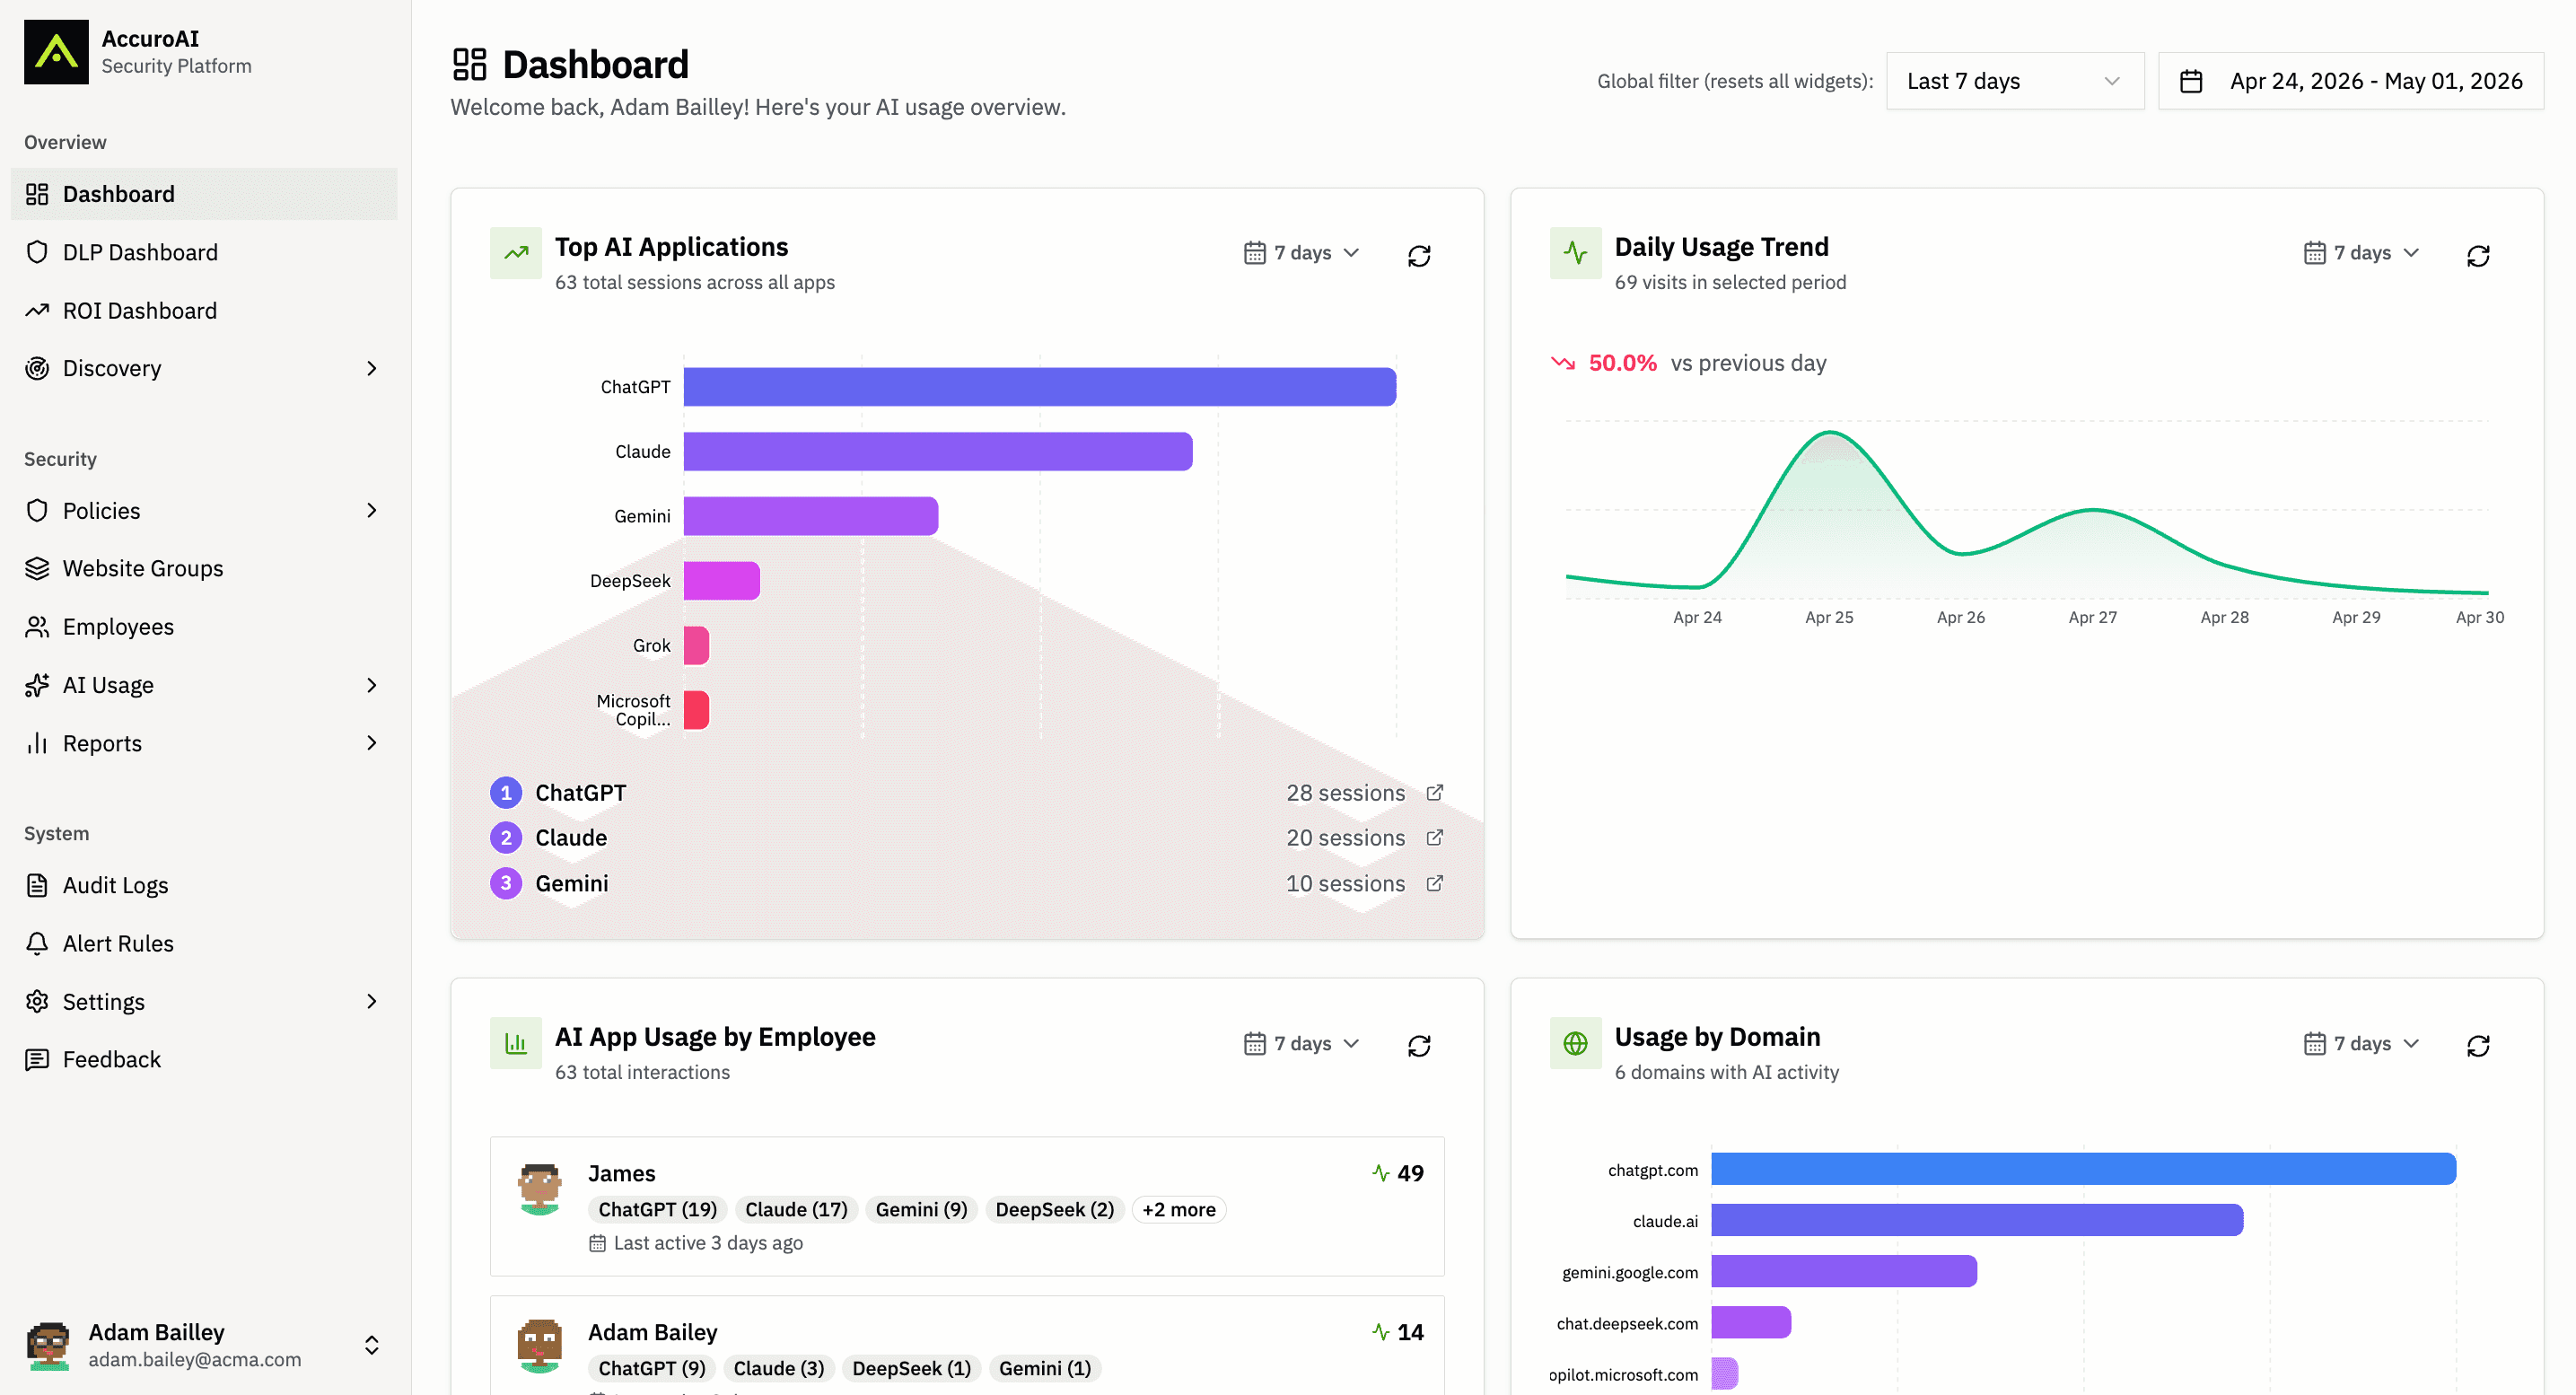
The first day AI becomes measurable.
Real-time visibility across every AI interaction, user, and application. The moment AccuroAI is live.
Free guides. The latest research.
The field guide for security leaders: operating model, frameworks crosswalked, benchmarks, and a ready-to-send vendor RFP.
The state of shadow AI, DLP, and agent governance, with a 90-day implementation roadmap.
Network proxies and browser extensions miss most of what happens inside desktop AI apps, local models and coding agents. Governing them takes a component on the laptop that discovers installed AI apps and agents and enforces policy at the point of use. This guide compares what each control layer sees and lays out the rollout through MDM, or directly on devices for a pilot, with a one-week plan.
To block personal ChatGPT accounts and keep the company one, use each vendor's control: an allow-list header your proxy injects for OpenAI, Anthropic and Google, or Entra Tenant Restrictions v2 for Microsoft Copilot. These work only where a TLS-inspecting proxy or Microsoft's client sees the traffic. We compare all four from the vendors' own docs and set out what enforcing by signed-in account adds.
Do AI coding assistants leak more secrets? For the one agent measured in public, yes: GitGuardian found Claude Code-assisted commits leaked secrets at 3.2% against a 1.5% baseline, and 24,008 secrets sitting in MCP configuration files. The second problem is the instruction files, CLAUDE.md, AGENTS.md, .cursor/rules and copilot-instructions.md, which every agent reads as instructions and which travel with the repo. We map both to OWASP ASI01 and ASI04, compare Cursor, Claude Code and the Copilot cloud agent from their own docs, and set out five controls.