ChatGPT Work: A Security Review for Enterprise Admins
ChatGPT Work is not a bigger chatbot — it's an autonomous process acting under employee identity across your SaaS estate and the open web. The security review to read before saying yes: real credit for OpenAI's controls, five surviving risks, eight hardening steps.
J
James Okafor
Field CISO
Aug 6, 2026
OpenAI launched ChatGPT Work on July 9, 2026, and it is not a bigger chatbot. It is an autonomous workspace agent that connects to your apps and files, runs independently for hours, and comes back with finished artifacts: spreadsheets, documents, working web apps. Your employees are already asking for it; some already have it. This is the security review we would want before saying yes: what it actually is, the admin controls OpenAI ships, the five risks that survive those controls, and a hardening checklist for the rollout.
Last verified: August 6, 2026. This product is weeks old and moving fast, reverify controls against OpenAI's current admin documentation before locking policy.
What ChatGPT Work actually is
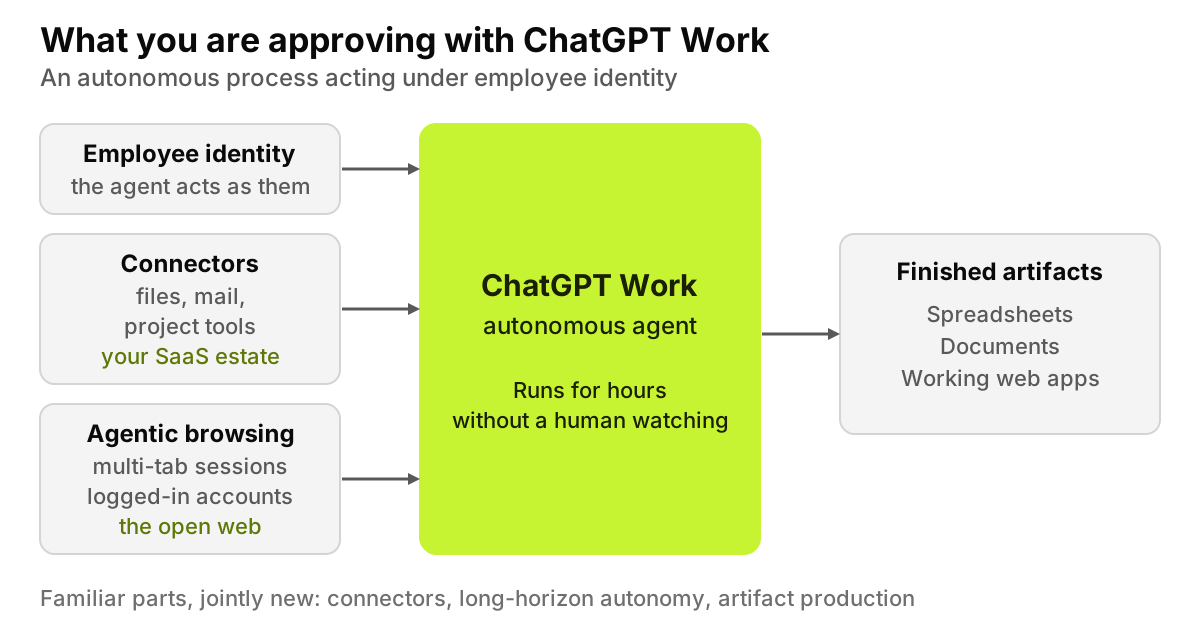
Built on the GPT-5.6 family, ChatGPT Work combines three things that are individually familiar and jointly new: connectors into enterprise systems (files, mail, project tools: including SharePoint-class sources), long-horizon autonomy (multi-hour runs without a human watching), and artifact production (it does not suggest the spreadsheet; it builds it). Add the August change that folds agentic browsing into ChatGPT itself, with multi-tab sessions and logged-in account access, following the Atlas browser's retirement on August 9, and the surface you are approving is: an autonomous process, acting under employee identity, across your SaaS estate and the open web.
Figure 1. Each part is familiar on its own. Together they make a process that acts as an employee across SaaS and the web, and that process is what you are approving.
The admin controls OpenAI ships (credit where due)
Spend and usage controls: workspace defaults, per-group limits, credit-request flows.
Action preauthorization, sensitive actions can require human approval before the agent executes.
Per-connector tool scoping, admins choose which tools and connectors each workspace exposes.
The Enterprise baseline: SSO/SCIM, no training on business data, compliance API access, audit logs.
This is a more serious enterprise posture than most agent launches ship with. It is also (as OpenAI would likely agree) a set of controls inside one vendor's product, which is exactly the scope limitation the rest of this review is about.
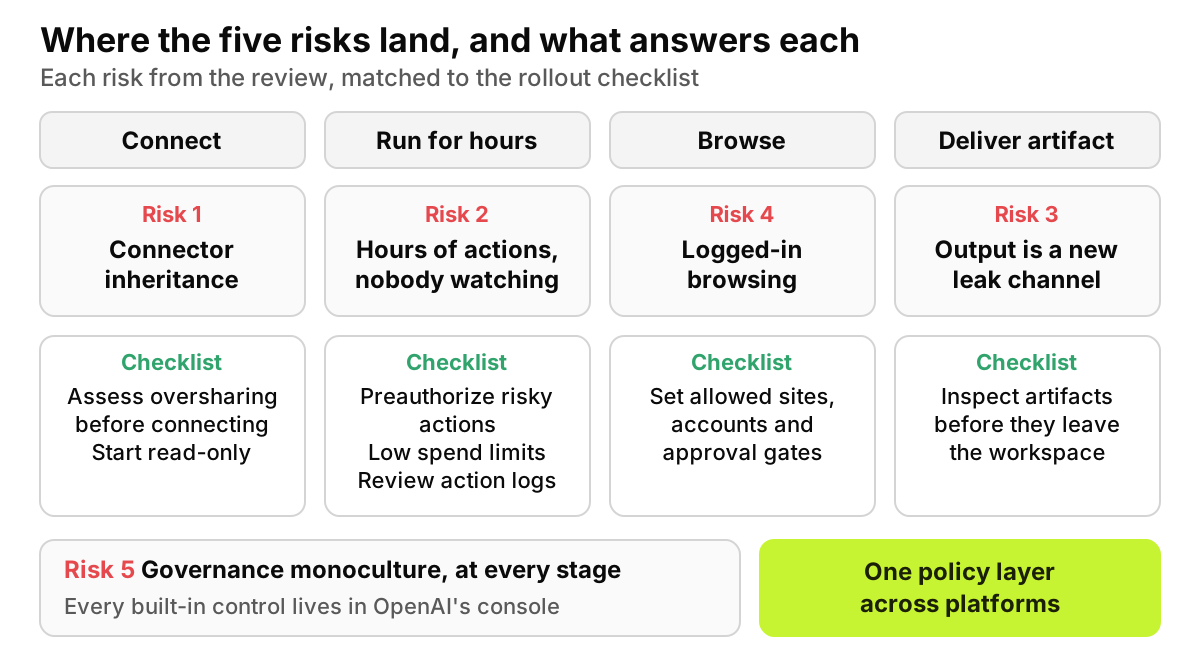
The five risks that survive the built-in controls
1. Connector inheritance is the new oversharing
A connector scoped to "what the user can access" inherits every permission mistake in the connected system, the same mechanism that made Copilot surface a decade of SharePoint sprawl, now replayed outside Microsoft's trust boundary. If you have not run an oversharing assessment on the systems you are about to connect, the agent will run one for you, in production.
2. Hours of actions, nobody watching
Multi-hour autonomy means the human-review moment moves from "each response" to "the finished artifact", and everything in between happened unsupervised. 1Password's July survey found 47% of developers had already seen agents take unintended actions after following instructions embedded in webpages, documents, or tool outputs. Long-horizon runs multiply the exposure window for exactly that class of indirect injection.
3. The output is a new leak channel
Prompt-side DLP inspects what goes in. ChatGPT Work's product is what comes out: generated spreadsheets and apps that can aggregate sensitive data from many connected sources into one exportable artifact. Response-side inspection stops being optional when the response is a file.
4. Browsing with logged-in sessions
Agentic browsing under employee sessions inherits the zero-click hijacking class demonstrated across agentic browsers at Black Hat last week, crafted page content overriding the user's actual intent. The mitigation posture (which sites, which accounts, which actions need approval) has to be yours, not just the vendor's.
5. Governance monoculture
Every control above lives inside OpenAI's console, covers only OpenAI's agent, and produces OpenAI's logs. Enterprises running Copilot and Claude alongside (which is most of you) end up with three consoles, three rulebooks, and no unified answer to "what did agents do across our estate this week?" That cross-platform layer is the part we build; the vendor consoles are the parts they build; you need both to be true.
The rollout hardening checklist
Run oversharing assessments on every system before connecting it, not after.
Start with read-only connectors; add write scopes per-workflow with named owners.
Turn on action preauthorization for anything destructive, external-facing, or financial.
Set spend limits low initially, runaway autonomy shows up on the bill before the audit.
Pilot with one team, review the full action logs weekly, not the artifacts, the actions.
Put response-side inspection on generated artifacts before they leave the workspace.
Update your AI acceptable-use policy: autonomy changes the "human review" clause materially.
Decide the browsing posture explicitly (allowed sites, logged-in accounts, approval gates) before the Atlas migration lands on your users on August 9.
Figure 2. Review the actions, not only the artifacts. The human review moment moves from each response to the finished output, and everything in between ran unsupervised.
Verdict
ChatGPT Work is the most enterprise-ready autonomous agent launch to date, and the productivity claims are not hype. Approve it the way you would approve a new employee with system access on day one: scoped credentials, supervised probation, and logs someone actually reads. The organizations that get hurt will be the ones that approved it as if it were a chatbot.
How AccuroAI helps
AccuroAI handles the part of this rollout that sits outside OpenAI's console. It shows which employees already use ChatGPT on personal accounts versus the company workspace, blocks the personal sign-ins on managed devices while the enterprise account keeps working, and redacts sensitive data from prompts and stops sensitive file uploads before they reach the workspace, using the same rules it applies to Copilot and Claude. That gives the governance-monoculture problem one rulebook and one audit trail; Workforce AI Governance explains how. Run it beside your ChatGPT Work cohort with a free 72-hour pilot.
FAQ
Is ChatGPT Work safe for enterprise use?
With the built-in controls configured, connector hygiene done first, and independent inspection of actions and outputs, yes, comparably safe to other governed automation. Out of the box with default scopes and unaudited connectors, no.
Does our existing ChatGPT Enterprise DLP cover it?
Prompt-side inspection carries over; the new exposure is connector inheritance, long-run actions, and generated artifacts. If your current control only watches the paste, it watches the smallest part of this product.
How is this different from Copilot?
Copilot grounds in your M365 tenant under Microsoft's compliance stack; ChatGPT Work reaches the same data through connectors outside that boundary, with longer autonomy. Run both? Then you have precisely the dual-assistant governance problem, one policy layer across both is the sane architecture.
What should we monitor from day one?
Connector scope changes, preauthorization bypasses, artifact exports, and any action following untrusted web content. If those four are logged and reviewed, you will catch the failure modes that matter early.
One item on the rollout checklist deserves more than a line: the acceptable use update. Review clauses written for chat assumed someone read every reply, and ChatGPT Work returns a finished artifact hours later. The review section of our acceptable use policy template names an accountable person before output reaches a customer or shapes a decision about someone, and its agent section grades actions from read only through sandbox and production writes to irreversible steps that need human sign-off as they execute. Those grades track the connector sequence above.