The problem
Governance that lives in a document isn’t governance.
You can’t see what’s in use
Sanctioned tools, shadow tools, browser extensions, agents. Most orgs can name a fraction of the AI actually touching their data.
Policy lives in a PDF
The AI use policy exists, as a document nobody enforces. There is no engine turning it into decisions at the moment of use.
Audits are a scramble
Every framework asks for evidence of control. Without continuous collection, each audit becomes weeks of screenshots and spreadsheets.
Policy to proof
Every prompt. Every file. Inspected. Before it reaches the model.
Select a policy rule and watch it fire on a live example: inspected inline, enforced before the model sees a byte, evidence logged as it happens.
Capabilities
Discovery to defensible, on one policy engine.
Every capability below feeds the same console, the same policy engine, and the same audit trail, so a discovery today is an enforced policy this afternoon and board-ready evidence at quarter end.
Shadow AI discovery
Continuous inventory of every AI tool, extension, and agent in use, attributed to users and business units.
Policy engine
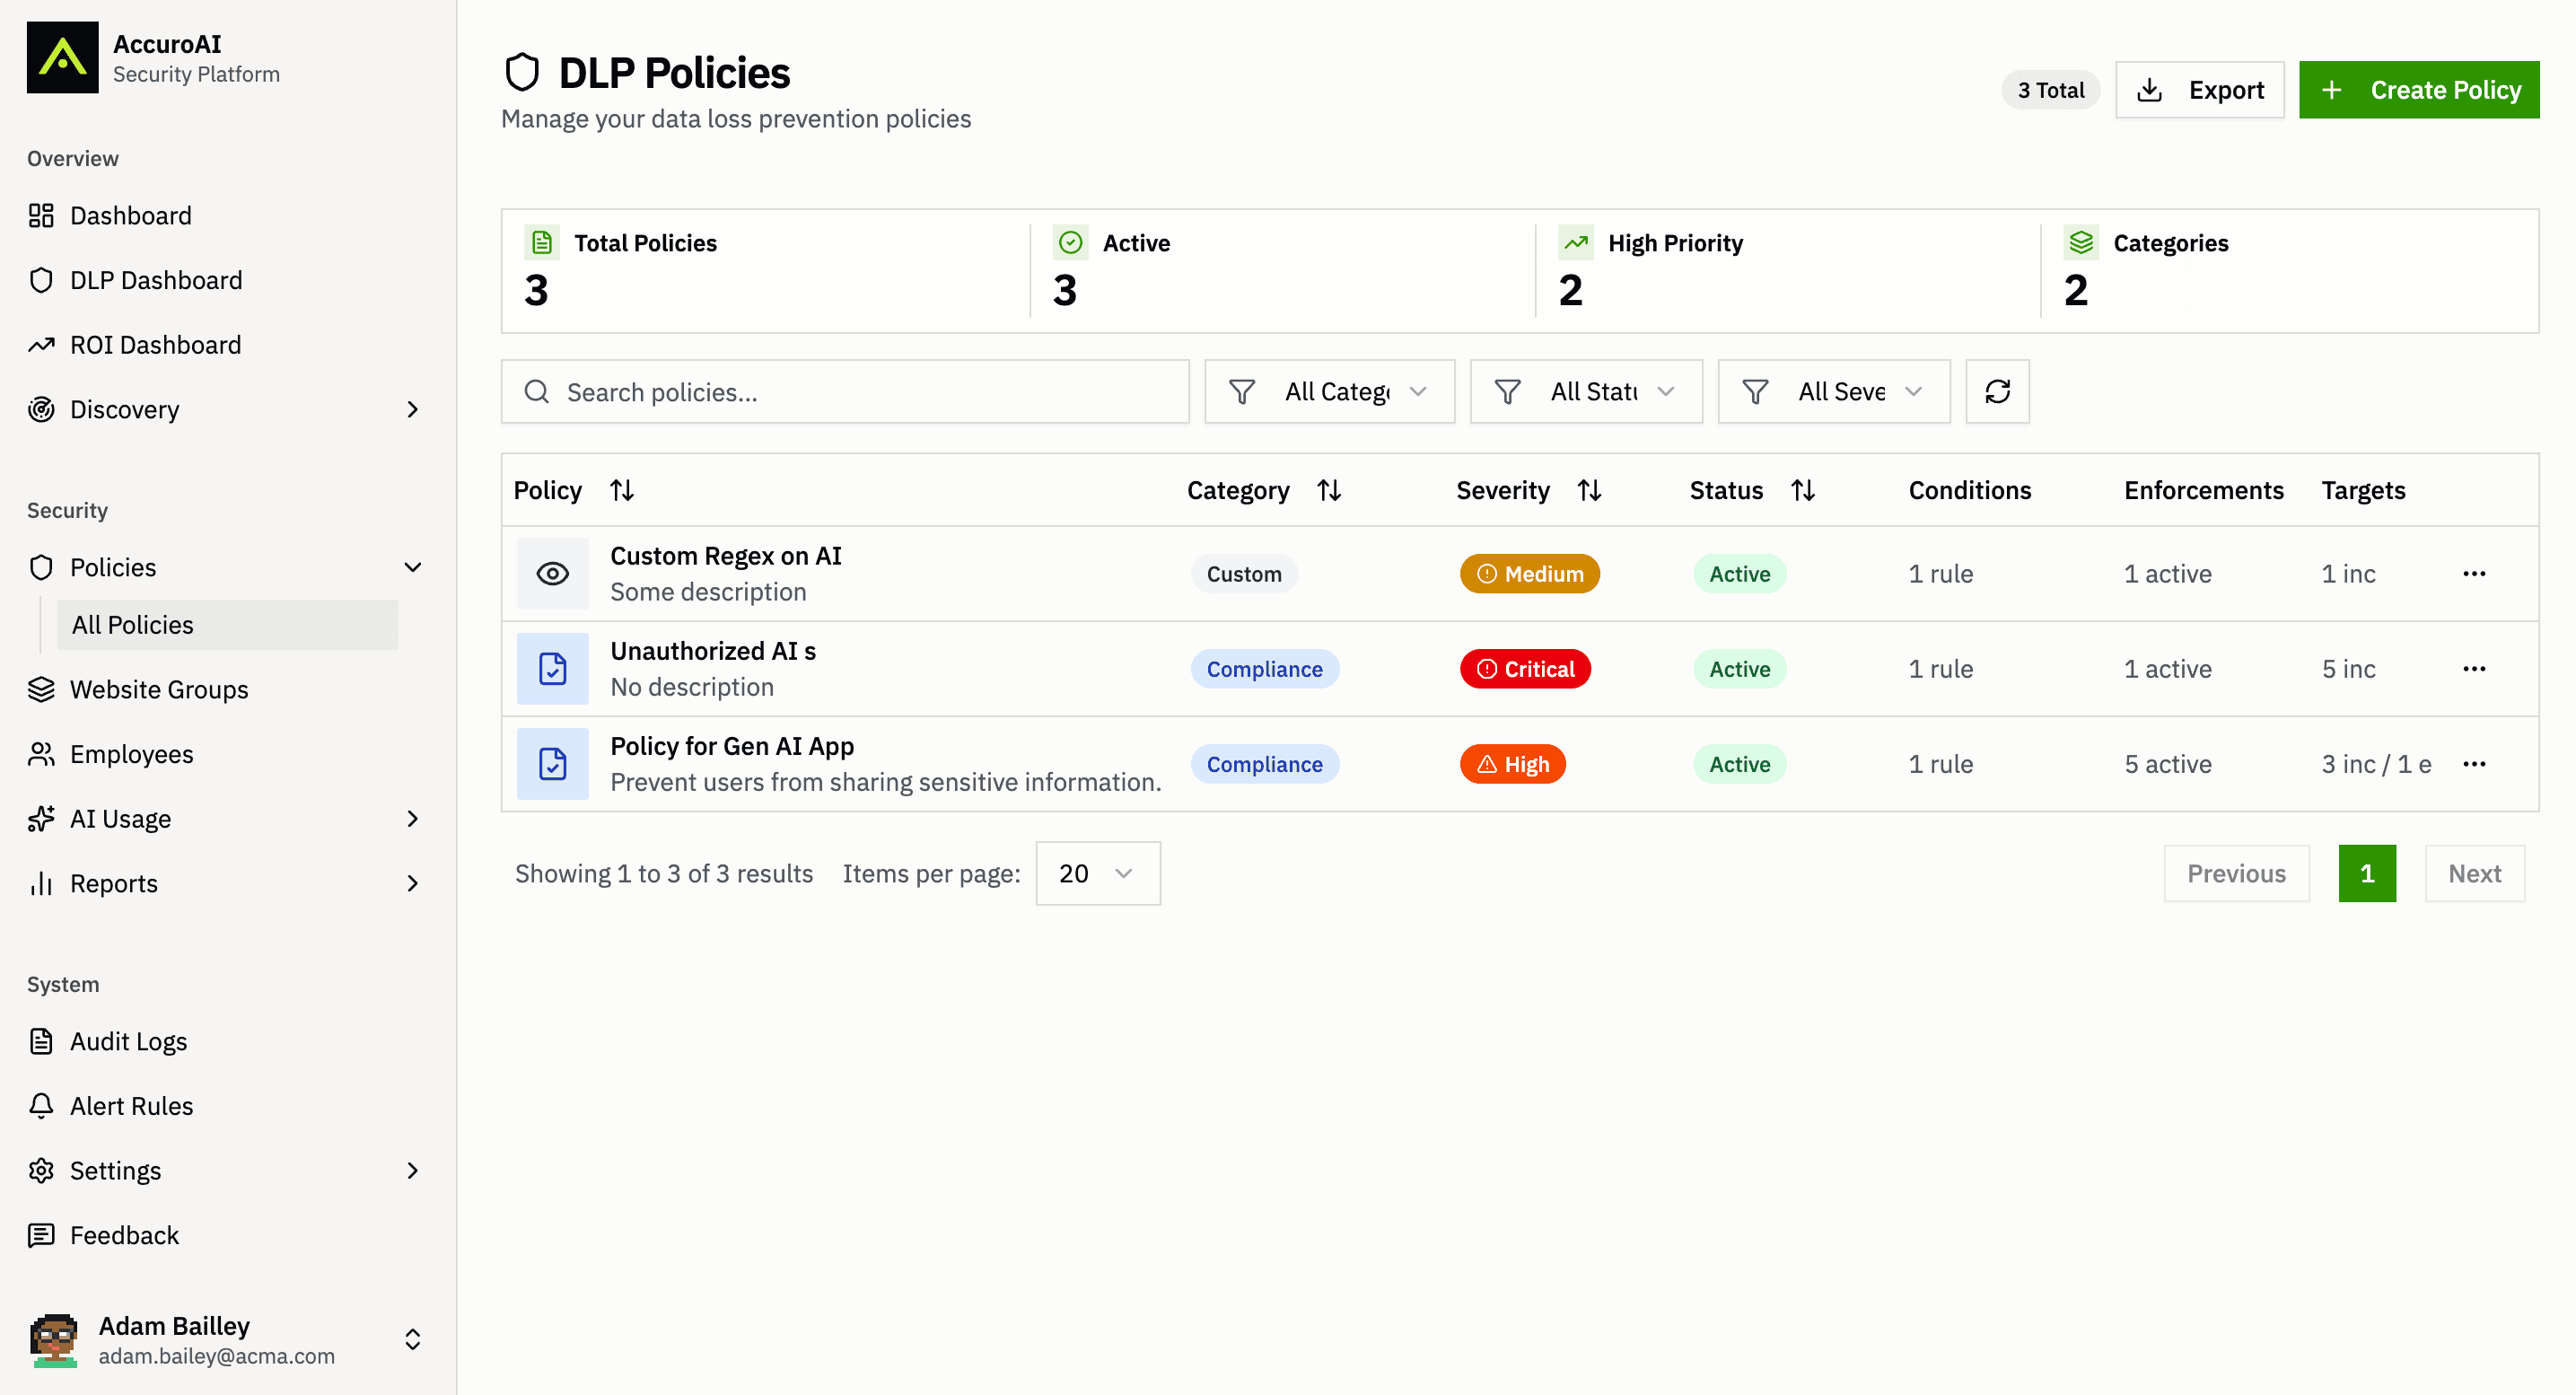
Write policies in plain language or YAML. Version-controlled, staged rollouts, enforced inline at the moment of use.
Compliance automation
Every enforcement decision becomes evidence, auto-mapped to the frameworks your auditors ask about.
Audit & evidence
Prompt logs, redaction records, and full decision trails: exportable in one click, retained on your schedule.
Framework mappings
SOC 2, ISO 27001, ISO 42001, NIST AI RMF, EU AI Act, GDPR, HIPAA, PCI DSS: mapped once, kept current.
Executive reporting
Board-ready AI risk summaries generated automatically. Hand them over unmodified.
Personal vs corporate accounts
Keep the sanctioned corporate workspace allowed and inspected. Block personal logins to the same tool, so nobody is pushed onto an unmonitored path.
Obfuscation-aware detection
Classifiers read decoded content, not the literal string, so Base64 and Unicode tricks are redacted in real time. Detection is not English-only.
No TLS interception
Enforcement runs at the point of use, not a man-in-the-middle proxy. No corporate root certificate on employee devices, nothing that breaks certificate pinning.
Platform
One platform. Every surface.
The same policy engine, console, and audit trail also cover the rest of your AI surface: